Authentication (OATH)
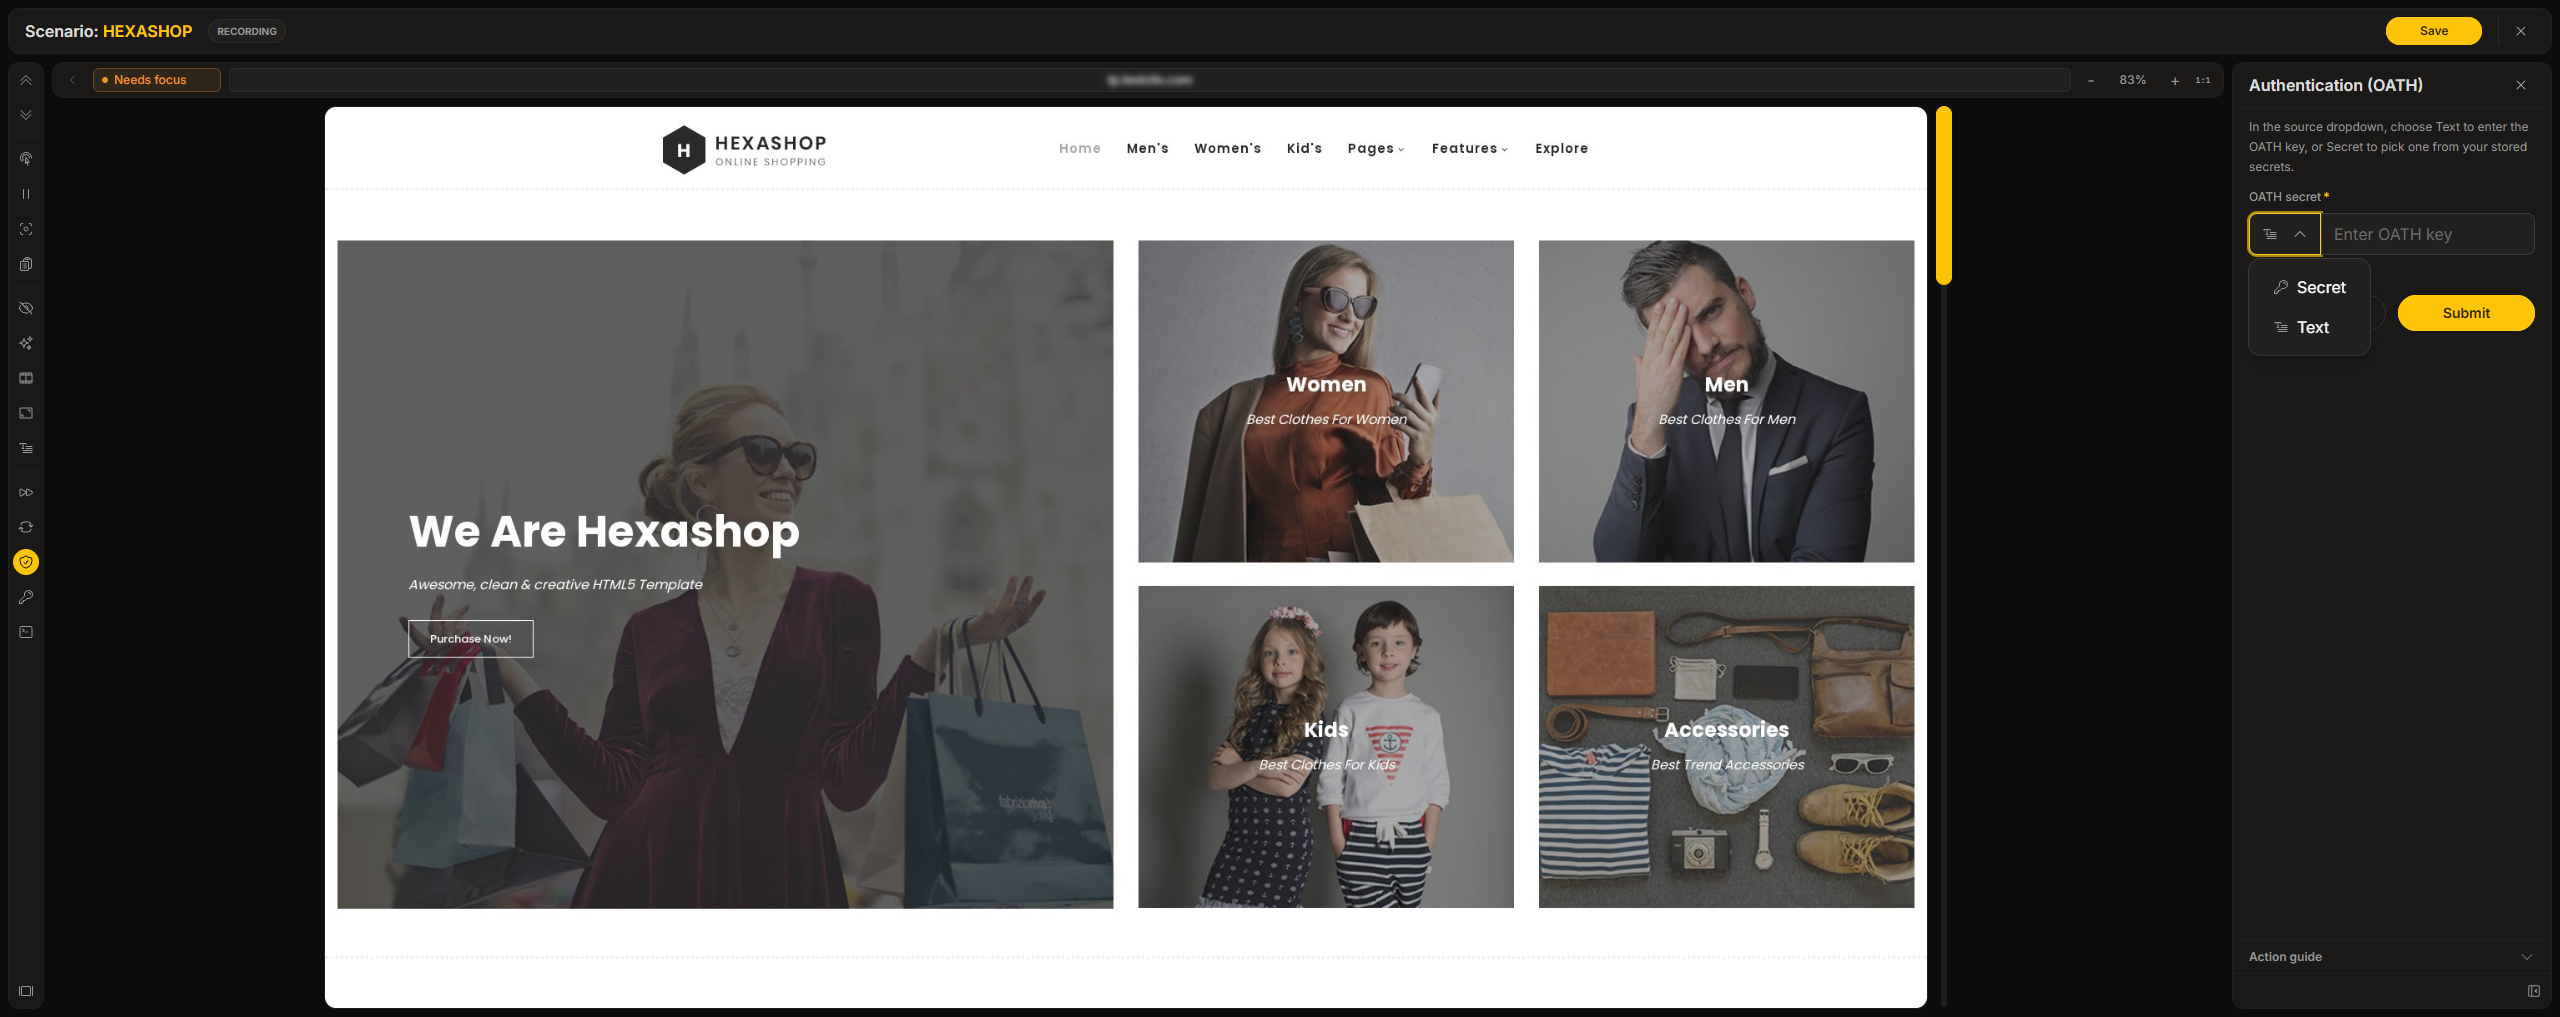
The OATH action lets your scenario pass a time-based one-time password (TOTP) step. Many services use TOTP as a multi-factor authentication (MFA) method during login - apps like Google Authenticator, Authy, or Microsoft Authenticator generate a short-lived code that the user must enter to prove their identity. The OATH action automates this step so you can monitor MFA-protected login flows without manual intervention.
How to add an OATH step
Section titled “How to add an OATH step”The generated code is pasted into whichever input field is currently active on the page. Before adding the OATH step, click on the MFA code input field to make sure it has focus.
- In the recorder, make sure you are in Live mode.
- Click on the TOTP input field on the page so it receives focus.
- In the toolbox, select Add OATH. If it is not visible, open More actions.
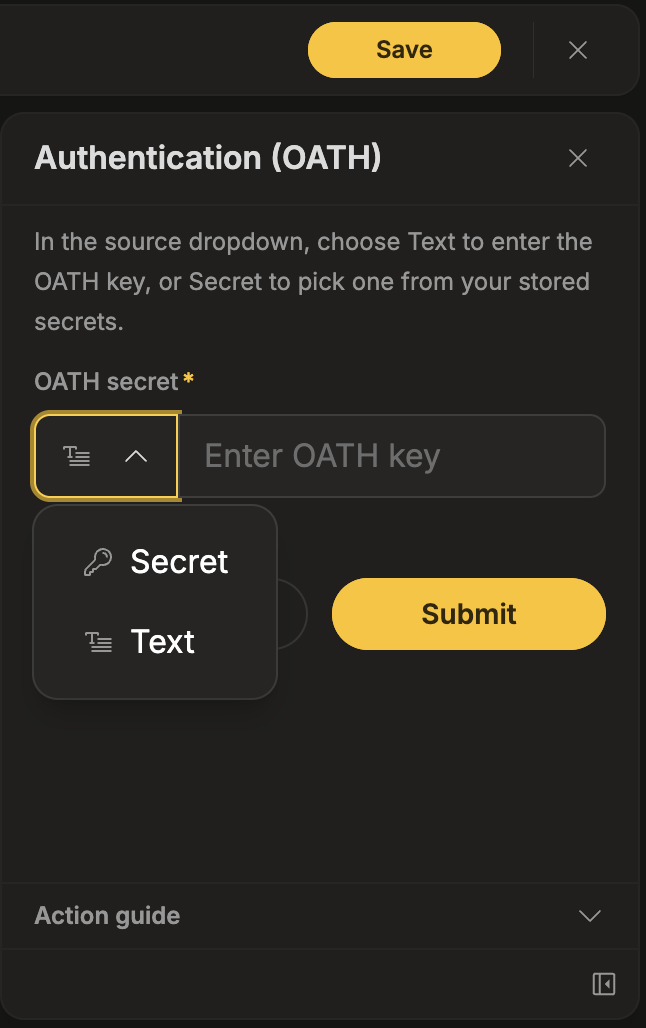
- Choose the key source:
- Text - enter the Base32-encoded TOTP key directly. The key is masked by default - use the show/hide toggle to check what you typed.
- Secret - select a secret stored in the current project. You can create one from the same picker if needed. See Using a stored secret.
- Enter or select the TOTP key.
- Click Submit.
The recorder generates a fresh code from the key, types it into the active input field, and adds an Authentication event to the timeline. If you entered the key as Text, the key itself is stored with the event - it is not added to the project’s secrets. If you picked a stored secret, only the reference to it is stored.
How it works
Section titled “How it works”During monitoring, TestCLIX generates a new TOTP code using the selected key and the current time. Because TOTP codes are time-based and deterministic, this produces a valid code for the current time window without any manual input.
Only the TOTP key source is stored - never the generated code itself. A text key is saved with the recording. A project secret is referenced by its stored secret ID and resolved when the scenario runs. Each run produces a fresh code valid for that moment.
Using a stored secret
Section titled “Using a stored secret”Instead of entering the key as Text, you can set the source to Secret and point the OATH step at a secret stored in the project. The key is then held in project settings rather than in the scenario, and it is resolved on the server at run time - the recorder never displays it.
This is worth doing when:
- the same MFA account is used by more than one scenario
- you rotate the key and do not want to re-record every scenario that uses it
- you would rather not have the key readable inside the recording
The picker is searchable and lists the project’s stored secrets. If the secret does not exist yet, you can create it without leaving the recorder - see below.
Create a secret from the picker
Section titled “Create a secret from the picker”At the top of the secret list is a Create secret entry. It opens the Secrets dialog, where you add the secret with the same form as on the Secrets settings tab.
Once you save it, the new secret is selected in the OATH step automatically - you do not have to pick it from the list again.
How the step shows its secret
Section titled “How the step shows its secret”Once recorded, an OATH step that uses a stored secret displays the secret’s name as
Name: <secret name> on the step card and in the timeline status bar.
If the secret has since been deleted, the step shows “Secret deleted” in red instead. To repair it, change the secret on the step.
Changing the key later
Section titled “Changing the key later”You do not have to re-record an OATH step to change the key it authenticates with. Select the event in the Session Timeline, choose a new Text or Secret value in Event Preview, and click Save secret - see Change a Step’s Secret.
Best used for
Section titled “Best used for”- Logging into accounts protected by TOTP two-factor authentication
- Passing MFA challenges during automated monitoring of login flows
- Monitoring admin panels, banking portals, or any service that requires a one-time code at sign-in
Common errors
Section titled “Common errors”| Error | Meaning | What to do |
|---|---|---|
| Error generating token | The secret is invalid or incorrectly formatted. | Verify the TOTP secret is a valid Base32-encoded key from your authentication provider. If the step uses a stored secret, check that the stored value is the key itself and not a generated code. |
| Secret deleted | The recorded event references a project secret that no longer exists. | Select another stored secret or enter a valid Text key in Event Preview. See Change a Step’s Secret. |
Caveats
Section titled “Caveats”- Make sure the target input field is focused before adding the OATH step. The generated code is typed into whichever field currently has focus.
- The system clock on the playback environment must be accurate. TOTP codes are valid only within a short time window (typically 30 seconds), so clock drift can cause codes to be rejected.
- If the application rejects a code that was already used within the same time window, playback may fail. This can happen when a scenario is replayed very quickly after a previous run.